
Stellar Cyber has announced Stellar Cyber 7.0, a major platform release designed to transform the concept of the Human-Augmented Autonomous Security Operations Center (SOC) into a practical and scalable operating model. The new version combines AI-powered case triage, measurable SOC workflows, expanded investigative evidence, automated response capabilities, and enhanced APIs to help organizations operate security operations more effectively at scale.
The release reflects a shift in cybersecurity operations from simply accelerating analysts’ work to delivering measurable security outcomes. Rather than focusing solely on collecting more data and generating more alerts, Stellar Cyber 7.0 enables security teams to identify what truly matters, understand the context behind threats, take appropriate action, and evaluate whether security operations are improving over time.
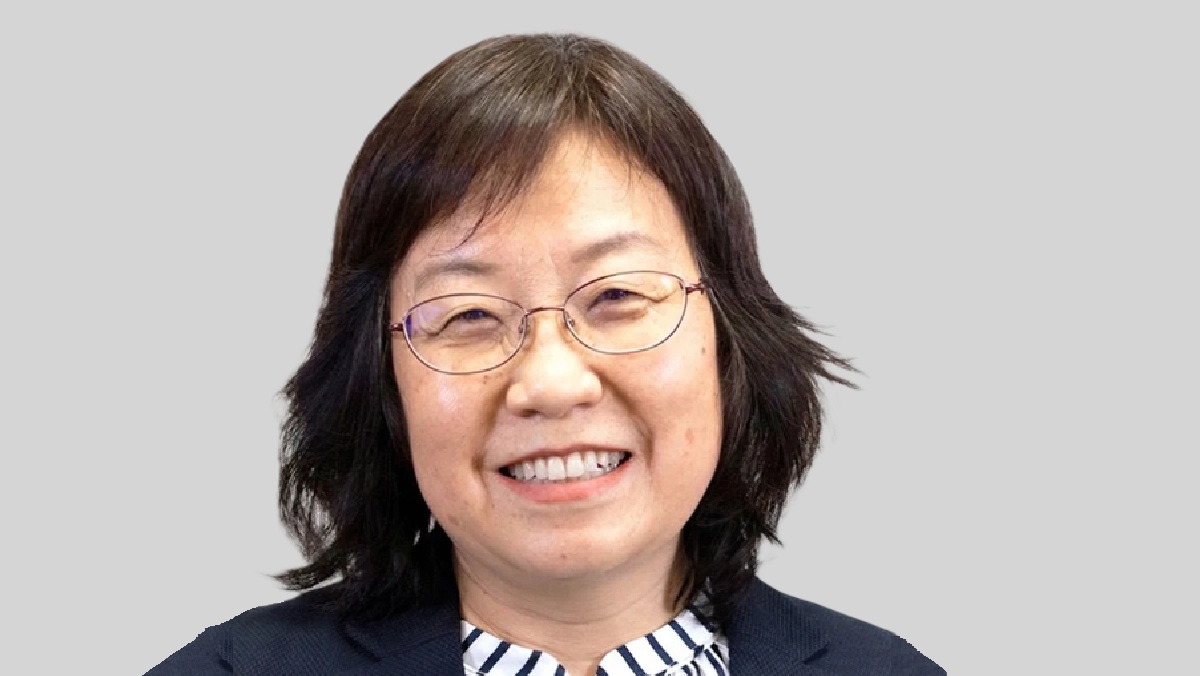
“Security operations has spent years focused on collecting more data and generating more detections,” said Aimei Wei, Founder and CTO of Stellar Cyber. “The next era is about outcomes. Did we identify the real attack? How quickly did we understand it? Did we take the right action? And are we improving over time? Stellar Cyber 7.0 brings those pieces together so organizations can safely automate more of the SOC while keeping human judgment where it matters most.”
A key feature of the new release is AI-driven case analysis and automated triage at the case-queue level. This allows organizations to determine where automation should be applied based on risk and operational requirements. Managed Security Service Providers (MSSPs) can automatically prioritize and assess high-risk incidents across multiple customer environments, while enterprise security teams can focus their attention on the most critical threats.
To improve visibility into SOC effectiveness, Stellar Cyber 7.0 introduces Case Metrics, enabling organizations to measure operational milestones such as analyst acknowledgment times and case-resolution speed. These insights help security leaders identify bottlenecks, evaluate automation effectiveness, and measure service-level performance.
The platform also strengthens investigation and response capabilities through enhanced malware sandbox evidence, network payload visibility, and direct access to the original records behind correlated detections. New response integrations with Microsoft Defender for Endpoint, Fortinet FortiGate, and Cybereason allow analysts to move more quickly from investigation to containment.
Additionally, expanded APIs, improved System Action Center functionality, and enhancements to Parser Studio help MSSPs and large enterprises automate administrative tasks and manage security operations more efficiently. Together, these capabilities enable organizations to operate a more autonomous, measurable, and scalable SOC while continuing to leverage their existing security investments.